Empowering organizations through nine integrated Governance, Risk & Compliance services designed to strengthen accountability, manage enterprise risks, ensure regulatory compliance, and drive sustainable business performance.
Implement, train, audit, certify and improve. We support organizations across the full lifecycle of ISO management systems, from gap analysis and implementation to internal audit and certification through international certification partners.
International best practices
Improved performance
Stronger trust and credibility
ISO services: from gap analysis to continual improvement
01
Gap Analysis & Readiness Assessment
Clause-by-clause assessment of current practices, maturity and gaps, with a prioritized roadmap to certification.
02
Management System Design
Management systems built around your actual processes, risks and objectives, not unnecessary documentation.
03
Implementation Support
Hands-on support to operationalize the system, deploy controls and build effective implementation evidence.
04
Integrated Management Systems (IMS)
Multiple standards combined into one efficient system with shared risk, audit, CAPA and management review.
05
Internal Audit
Independent internal audits aligned with ISO 19011 to evaluate conformity, effectiveness and certification readiness.
06
Certification Readiness & Support
Preparation for Stage 1 and Stage 2 certification audits, from readiness review to corrective-action support.
07
Certification Transfer Support
Smooth transfer of an existing accredited certification, coordinated with the applicable certification partner.
08
Post-Certification & Continual Improvement
Ongoing support after certification to keep your management system effective and improving.
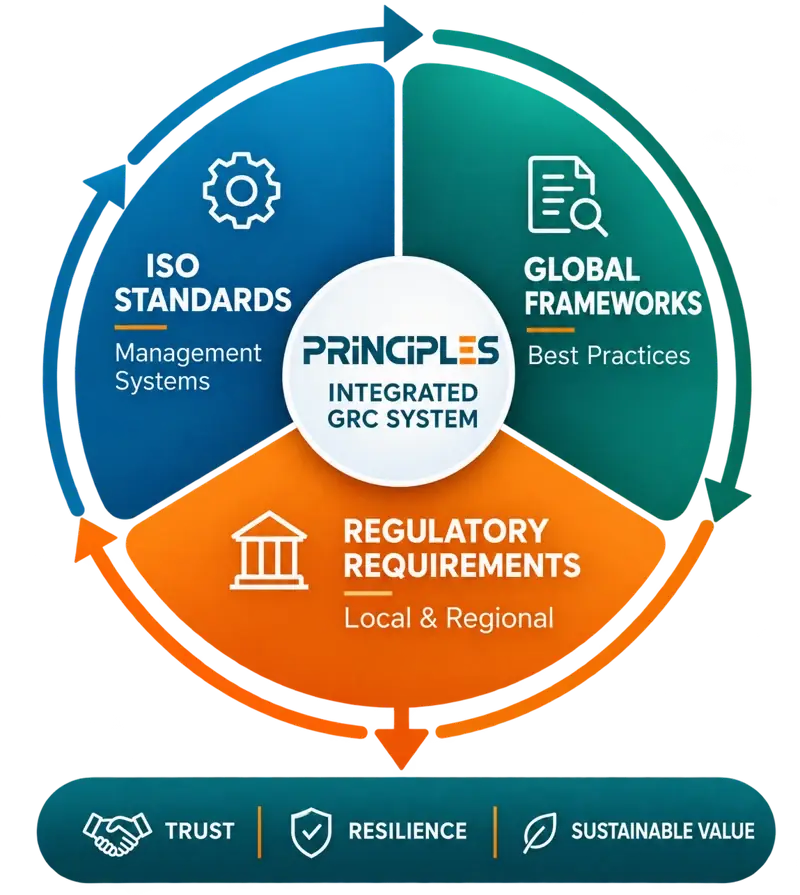
Standards framework: mapped to the level where they create value
01
Organization-wide governance & management systems
Strategic direction for a resilient, compliant organization
Enterprise / Organization
Board · Leadership · All functions
ISO
ISO 9001
Quality Management
ISO
ISO 14001
Environmental Management
ISO
ISO 45001
Occupational Health & Safety
ISO
ISO 22301
Business Continuity
ISO
ISO 31000
Risk Management
ISO
ISO 37001
Anti-Bribery
ISO
ISO 37301
Compliance Management
ISO
ISO 50001
Energy Management
ISO
ISO 55001
Asset Management
ISO
ISO 41001
Facility Management
ISO
ISO 44001
Collaborative Business Relationships
ISO
ISO/IEC 42001
AI Management
02
Department / function management systems
Effective management across key functions
IT / Digital
Information · Technology · Data · Digital services
ISO
ISO/IEC 27001
Information Security
ISO
ISO/IEC 27701
Privacy Information Management
ISO
ISO/IEC 27017
Cloud Security
ISO
ISO/IEC 27018
PII in Public Cloud
ISO
ISO/IEC 20000-1
IT Service Management
NIST
NIST CSF 2.0
Cybersecurity Framework
ISACA
COBIT 2019
IT Governance
AICPA
SOC 2
Readiness
PCI
PCI DSS
Payment Card Security
EU
GDPR
Data Protection & Privacy
HR / Customer / Governance
People · Clients · Compliance · Ethics
ISO
ISO 30409
Workforce Planning Guidance
ISO
ISO 10002
Complaints Handling
ISO
ISO 10004
Customer Satisfaction Monitoring
ISO
Anti-bribery & Compliance
Governance frameworks & regulatory alignment
03
Activity / process / sector-specific systems & guidance
Operational, industry and regulatory requirements
Operations / Sector
Production · Services · Supply chain · Projects
ISO
ISO 22000
Food Safety Management
FSSC
FSSC 22000 v6
Food Safety
ISO
ISO 13485
Medical Devices
ISO
ISO 21001
Educational Organizations
ISO
ISO 39001
Road Traffic Safety
ISO
ISO 21502
Project Management Guidance
ISO
ISO 19650
BIM (Information Management)
ISO
ISO 29001
Oil & Gas Sector QMS
SMIIC
HALAL
Certification Support
K
KOSHER
Certification Support
EU
CE
Marking Support
PRINCIPLES
Product / Sector
Compliance Support
Our approach
01
Gap Analysis
02
Implement
03
Train
04
Audit
05
Certify
06
Improve
Service 03 / 09
Digital Trust & Cybersecurity
Protect information, strengthen cyber resilience and enable trusted digital growth. We help organizations govern information security, cybersecurity, privacy, cloud and technology risk through integrated frameworks aligned with business objectives, international standards and regulation.
Secure operations
Resilient systems
Confident tomorrow
Digital trust services: from governance to cyber resilience
01
ISMS & ISO/IEC 27001
Design and implementation of risk-based Information Security Management Systems through to certification readiness.
02
Cybersecurity Governance
Governance structures that define cybersecurity accountability, oversight and decision-making.
03
Cyber Risk Assessment
Evaluation of cyber threats, vulnerabilities, business impacts and controls, followed by prioritized treatment.
04
NIST CSF & Cyber Maturity
Cybersecurity maturity assessments and improvement roadmaps using NIST CSF 2.0 and recognized frameworks.
05
Privacy & Data Protection
Privacy governance and data-protection controls aligned with applicable legislation, GDPR principles and ISO frameworks.
06
Cloud Security & Governance
Governance, risk and control frameworks for cloud environments aligned with ISO/IEC 27017 and 27018.
07
IT Governance & IT Service Management
IT governance and service management aligned with business objectives through COBIT and ISO/IEC 20000-1.
08
Cyber Resilience & Incident Readiness
Preparing your organization to respond to and recover from cyber events.
Standards, frameworks & alignment
01
ISO standards
ISO/IEC 27001Information Security
ISO/IEC 27017Cloud Security
ISO/IEC 27018PII in the Cloud
ISO/IEC 27701Privacy
ISO 22301Business Continuity
ISO/IEC 20000-1IT Service Mgmt
02
Global frameworks
NIST CSF 2.0Cybersecurity
COBIT 2019IT Governance
GDPRData Protection
PCI DSSPayment Card Industry
03
Regional requirements
NCA / NCSACybersecurity, KSA
SDAIAData & AI, KSA
SAMAWhere applicable, KSA
Other regionalCybersecurity regulations
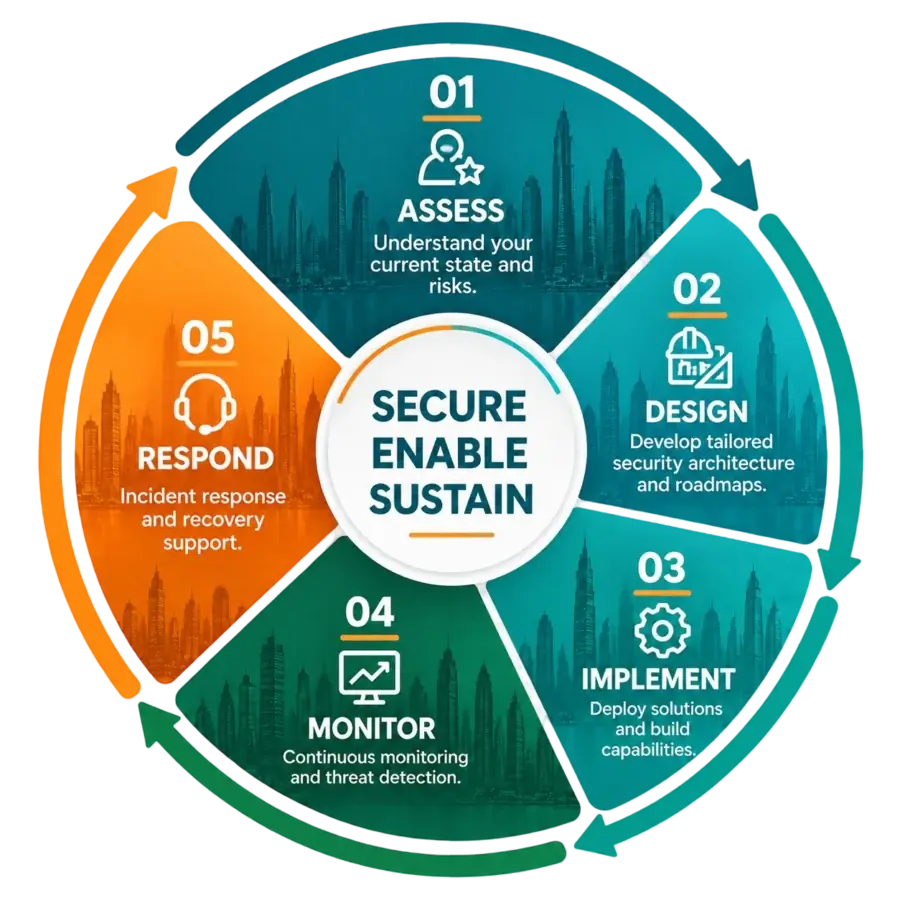
Our approach
01
Assess
02
Govern
03
Protect
04
Monitor
05
Respond
06
Improve
Service 04 / 09
Sustainability & ESG
Turn sustainability commitments into measurable performance. We help organizations build practical ESG governance, sustainability strategies, GRI-aligned reporting and measurable environmental and social performance, integrated with enterprise governance and risk management.
Measurable impact
Transparent reporting
Responsible growth
ESG services: from strategy to assurance readiness
01
ESG Strategy & Governance
ESG vision, governance, objectives and roadmaps aligned with business strategy.
02
Materiality Assessment
Identifying and prioritizing the ESG topics that matter most to your business and stakeholders.
03
GRI Sustainability Reporting
End-to-end support for sustainability reports aligned with GRI Standards.
04
ESG KPIs & Performance Management
Measurable ESG indicators with clear ownership, targets, data sources and dashboards.
05
Environmental & Social Impact
Assessing the impacts of operations, projects, services and supply chains and defining mitigation.
06
Carbon & Resource Efficiency
Structured measurement and management of energy, emissions, water, waste and resources.
07
ESG Risk & Compliance
Integrating sustainability risks, obligations and opportunities into enterprise risk and governance.
08
Sustainability Assurance Readiness
Improving the reliability of sustainability data and preparing for external assurance.
Key standards & frameworks
01
ISO standards
ISO 14001Environmental
ISO 50001Energy
ISO 26000Social Responsibility
ISO 37001Anti-Bribery
ISO 31000Risk
02
Global frameworks
GRISustainability Reporting
TCFDClimate Disclosures
SASBSustainability Accounting
CDPCarbon Disclosure
ISSBSustainability Standards
EU CSRDSustainability Reporting
UN SDGsSustainable Development
03
Regional requirements
NCESEnvironmental, KSA
SAMAWhere applicable, KSA
ZATCATax & Compliance, KSA
LocalEnvironmental regulations
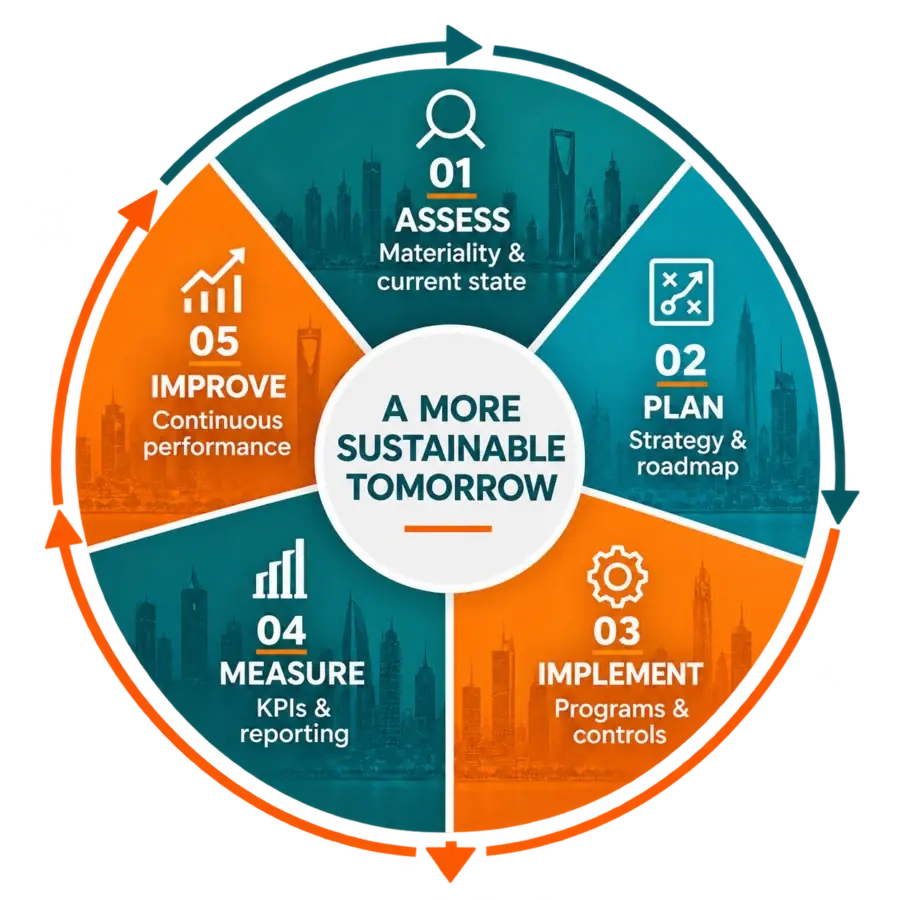
Our approach
01
Assess
02
Prioritize
03
Strategize
04
Implement
05
Measure
06
Report
Service 05 / 09
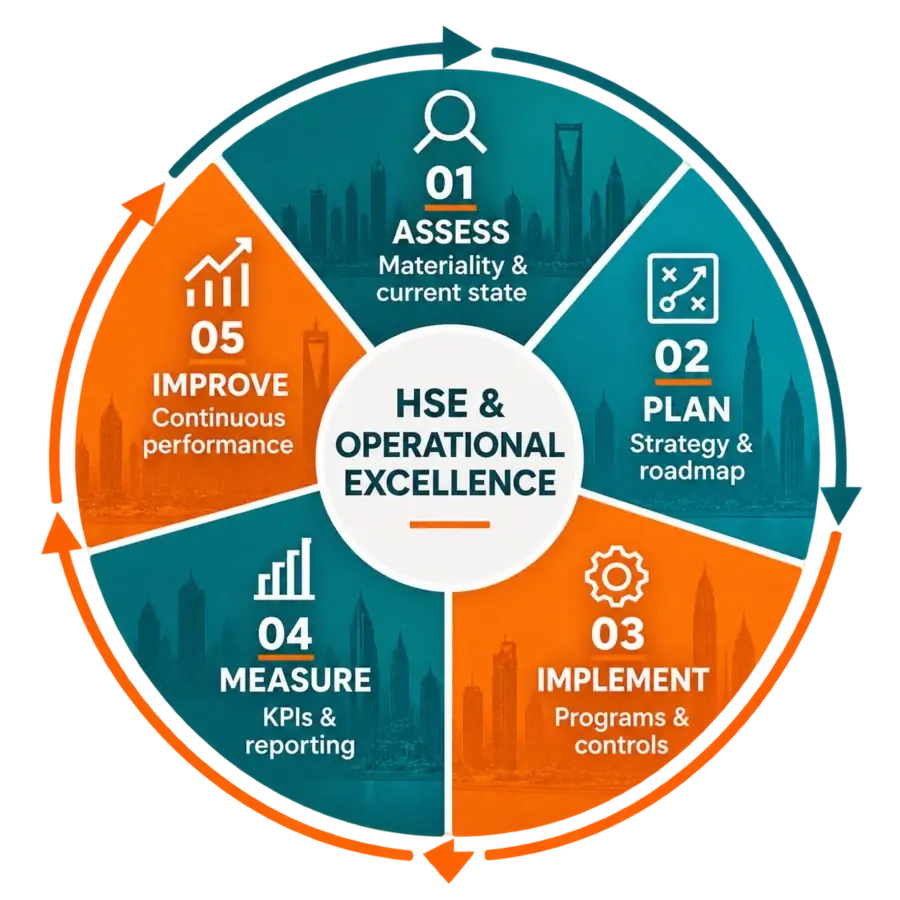
HSE & Operational Excellence
Safer people, controlled operations and stronger performance. We help organizations manage occupational health, safety, environmental and operational risks by turning requirements into practical controls at the workplace and operational level.
Safer people
Stronger operations
Measurable performance
HSE services: from risk assessment to independent audit
01
Occupational Health & Safety
Hazard identification, OH&S risk management, operational controls and performance monitoring.
02
Environmental Management
Management of environmental aspects, impacts, compliance obligations and environmental performance.
03
HSE Risk Assessment
Structured risk assessment using HIRA, JSA/JHA, TRA and other methods suited to the activity.
04
Operational Risk & Controls
Evaluating high-risk activities and critical controls to reduce incidents, disruption and losses.
05
Legal & Regulatory Compliance
Identification of applicable HSE legislation, legal registers and compliance evaluation.
06
Emergency Preparedness & Response
Emergency scenarios, response plans, drills and exercises that test organizational readiness.
07
Contractor HSE Management
HSE control across the contractor lifecycle, from prequalification to performance evaluation.
08
HSE Audit & Assurance
Independent site audits and compliance assessments of documented requirements and field implementation.
Standards, frameworks & alignment
01
ISO standards
ISO 45001OH&S
ISO 14001Environmental
ISO 9001Quality
ISO 31000Risk
02
Global frameworks
NFPAFire & Life Safety
IndustrySector-specific HSE
03
Regional requirements
HSE legislationNational & local laws
Our approach
01
Identify
02
Assess
03
Control
04
Implement
05
Verify
06
Improve
Service 06 / 09
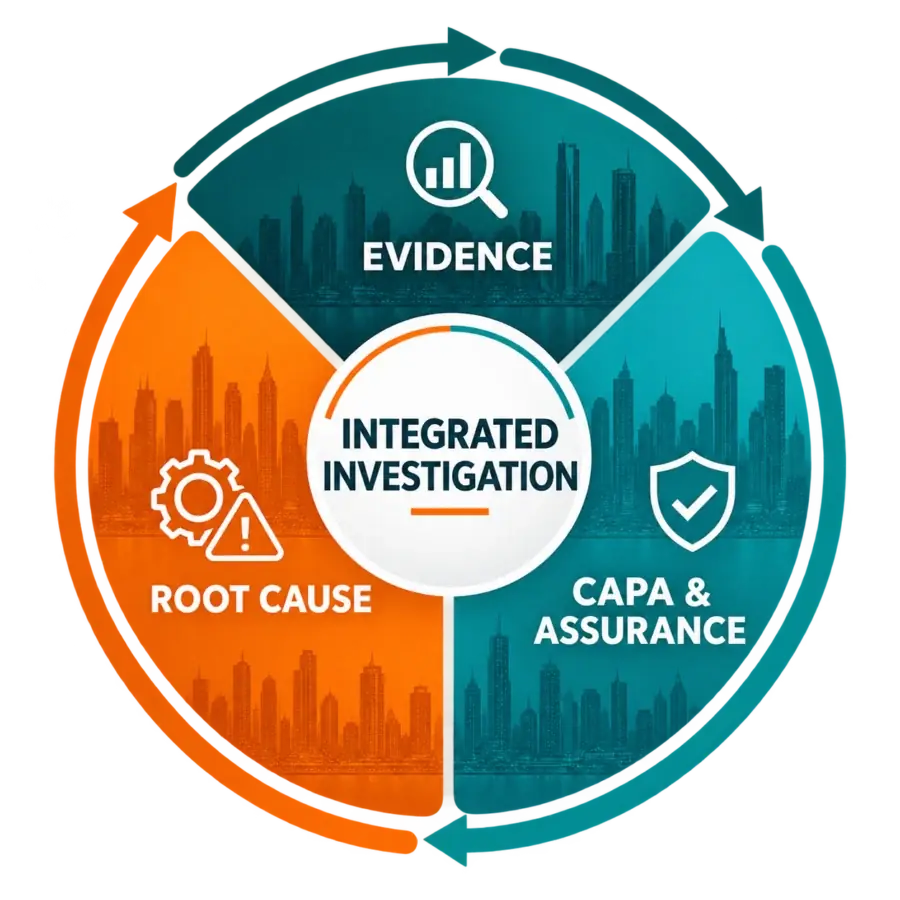
Accident & Incident Investigation
Independent investigation, evidence-based root cause and stronger prevention. When serious incidents occur, we provide multidisciplinary investigations that establish what happened, why it happened, which controls failed and what must change to prevent recurrence.
Independent analysis
Evidence-based findings
Actionable recommendations
Investigation services: from the event to root cause and CAPA
01
Fire & Explosion Investigation
Independent investigation of fire and explosion events, from scene assessment to corrective actions.
02
Oil & Gas / Process Safety Incidents
Specialist investigation of process operations, transfer systems and process-equipment incidents.
03
Crane & Lifting Incidents
Investigation of lifting incidents covering equipment, lifting plans, rigging and operator competence.
04
HSE Incidents
Independent investigation of injuries, LTIs, near misses and serious HSE events.
05
Environmental Incidents
Investigation of spills, releases, contamination and environmental-control failures.
06
Transportation & Logistics Incidents
Investigation of vehicle, tanker, fleet, warehouse and logistics incidents.
07
Cyber & Information Security Incidents
Assessment of governance and control failures, response effectiveness and business impact.
08
Business Continuity Events
Investigation of significant disruptions and recovery failures to strengthen resilience.
09
Mechanical & Electrical Failures
Technical investigation of equipment failures, maintenance history and operating conditions.
10
Root Cause Analysis & CAPA
Structured techniques that separate immediate, contributing and systemic causes.
Standards, techniques & alignment
01
ISO standards
ISO 45001OH&S Incidents
ISO 14001Environmental Incidents
ISO/IEC 27001Security Incidents
ISO 22301Continuity Events
ISO 31000Risk
ISO 9001Nonconformity & CAPA
02
Investigation techniques
5 WhyCausal Questioning
FishboneCause & Effect
FTAFault Tree Analysis
BarrierBarrier Analysis
BowTieThreats & Consequences
Human FactorsAnalysis
TimelineEvent Reconstruction
ChangeChange Analysis
03
Regulatory & industry
NFPAFire & Explosion
Process SafetyMOC, PTW, ESD
LegislationNational & local
Our approach
01
Plan
02
Collect
03
Interview
04
Analyze
05
Root Cause
06
Prevent
Service 07 / 09
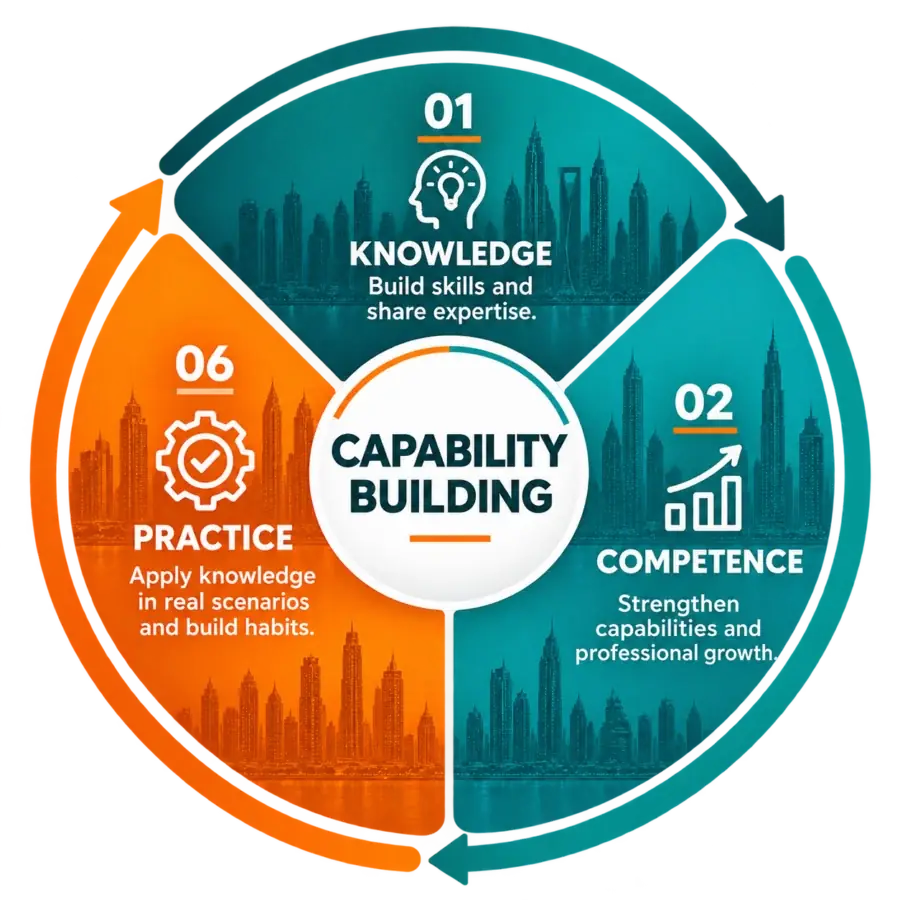
Training & Capacity Building
Build competence, strengthen culture and sustain performance. Practical professional development programs that turn international standards, frameworks and management requirements into skills people apply in their actual roles.
Accredited programs
Practical learning
Lasting competence
Training programs: from awareness to corporate academies
01
ISO Management Systems Training
Awareness, foundation, implementation and practitioner training across ISO standards.
02
Internal Auditor Training
Developing competent internal auditors who plan, conduct, report and follow up audits.
03
Lead Auditor & Advanced Programs
Advanced programs for professionals leading audit teams and complex audit programs.
04
GRC & Risk Management Training
Practical programs on governance, ERM, compliance, internal controls and risk treatment.
05
Cybersecurity & Digital Trust Training
Information security, cybersecurity governance, privacy, cloud security and digital resilience.
06
Business Continuity & Resilience Training
ISO 22301, BIA, continuity strategies, crisis management and exercises.
07
HSE & Operational Risk Training
Role-based training in safety, environment, hazard identification and operational controls.
08
ESG & Sustainability Training
Executive and practitioner programs on ESG governance, GRI reporting and sustainability KPIs.
09
Executive & Board Workshops
Concise executive sessions focused on strategic oversight and accountability.
10
Customized Corporate Academies
Organization-specific learning journeys that build sustainable internal capability.
Standards, formats & delivery
01
Standards covered
ISO 9001Quality
ISO 14001Environmental
ISO 45001OH&S
ISO/IEC 27001Information Security
ISO 22301Business Continuity
ISO/IEC 20000-1IT Service Mgmt
ISO 27701Privacy
ISO 31000Risk
ISO 19011Auditing
OtherCOSO ERM, NIST CSF, GRI
02
Program formats
AwarenessSessions
WorkshopsPractical Learning
PractitionerPrograms
Internal AuditorPrograms
AdvancedPrograms
ExecutiveBriefings
AcademiesCorporate
CoachingOn-the-job
03
Delivery options
On-siteAt your premises
Live onlineVirtual classroom
HybridCombined delivery
Our approach
01
Assess
02
Design
03
Deliver
04
Practice
05
Evaluate
06
Embed
Service 08 / 09
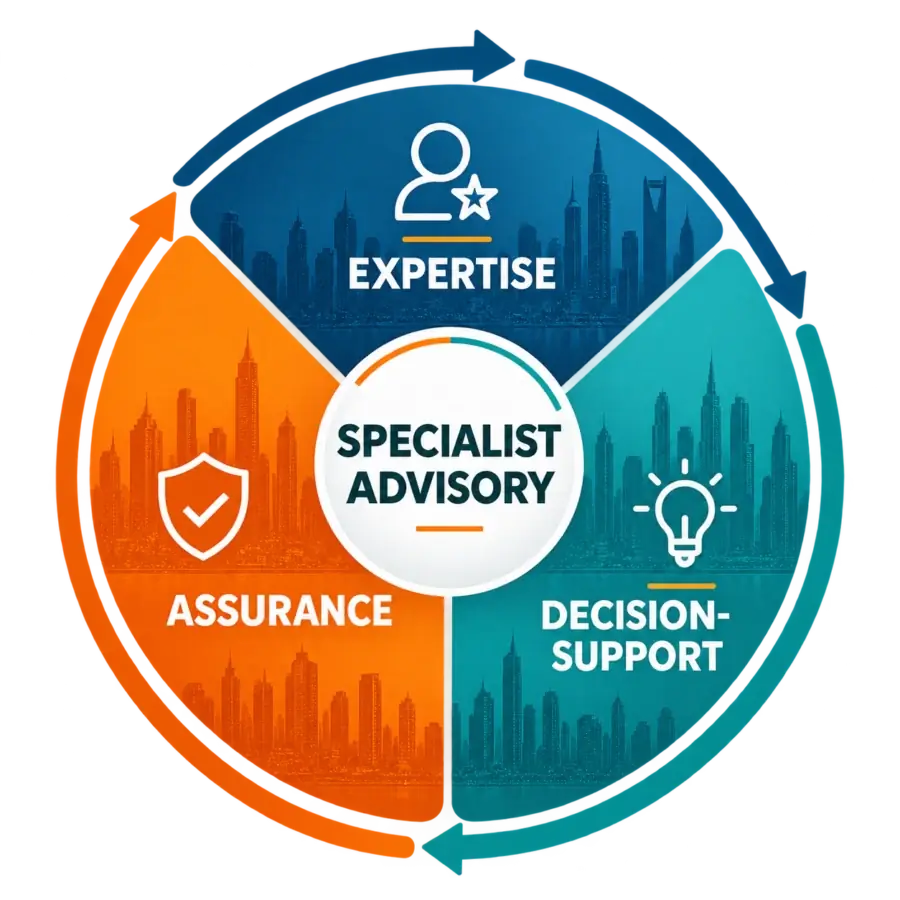
Technical & Specialist Advisory
The right expertise for complex decisions. Access to experienced consultants, technical specialists and subject-matter experts for complex, high-risk and non-routine assignments, combining technical expertise with governance, risk, compliance and assurance.
Independent expertise
Tailored solutions
Sector-specific knowledge
Advisory services: specialist expertise for complex decisions
01
Technical Advisory & Expert Support
Specialist expertise for complex technical, operational and management challenges.
02
Independent Technical Review
Independent review of technical deliverables to identify gaps and risks before critical decisions.
03
Regulatory & Standards Advisory
Translating standards and regulations into practical implementation requirements.
04
Project Technical Assurance
Independent expert oversight at defined project gates.
05
Product Compliance & Certification Support
Guidance on product standards, conformity requirements and certification pathways.
06
Specialist HSE & Process Safety Advisory
Specialist support for high-risk operations, process safety and fire safety.
07
Data Center & Critical Infrastructure Advisory
Resilience, continuity, security and governance for data centers and mission-critical facilities.
08
Expert-on-Demand / SME Support
Access to our specialists for projects or temporary capability needs.
09
Technical Due Diligence & Assessment
Independent technical and compliance assessments that support critical business decisions.
Standards, models & alignment
01
ISO standards
ISO 9001Quality
ISO 31000Risk
ISO 45001OH&S
ISO/IEC 27001Information Security
ISO 22301Business Continuity
ISO/IEC 17065Product Certification
02
Advisory models
On-demandTargeted intervention
Project-basedDedicated expertise
Independent reviewExternal assurance
RetainedOngoing access
Expert panelMultidisciplinary
03
Regulatory & technical
NFPAFire & Life Safety
ProductConformity regulations
LegislationNational & local
Our approach
01
Define
02
Match
03
Review
04
Advise
05
Assure
06
Transfer
Service 09 / 09
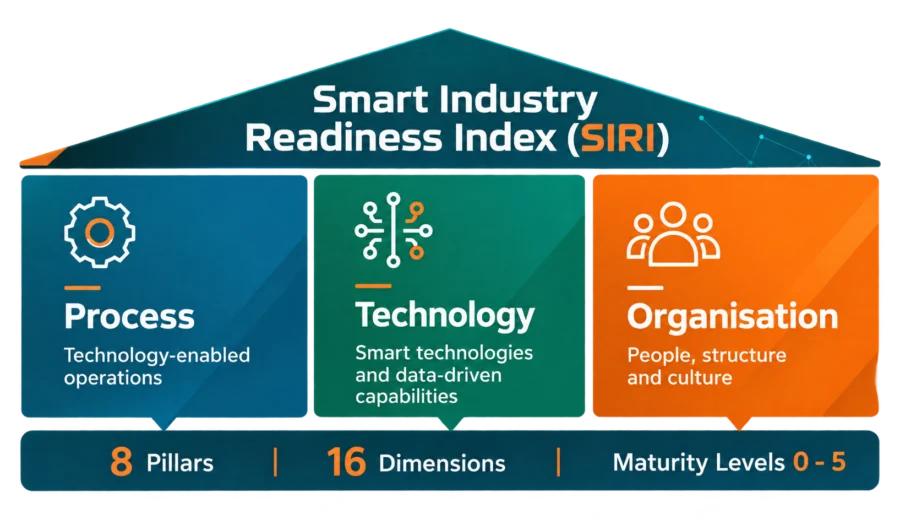
SIRI: Smart Industry Readiness Index 4.0
Assess maturity, prioritise investment and accelerate Industry 4.0. We support manufacturers in assessing, planning and accelerating their Industry 4.0 transformation using the Smart Industry Readiness Index (SIRI) framework.
Process: operations
Technology: smart & connected
Organisation: people & structure
SIRI services: from pre-assessment to official assessment
01
SIRI Readiness & Pre-Assessment
Scope definition, stakeholder alignment, evidence review and preparation for an official SIRI assessment.
02
Industry 4.0 Maturity & Gap Advisory
Structured review across the 16 SIRI dimensions covering Process, Technology and Organisation.
03
Transformation Prioritisation
High-impact improvement areas aligned with business objectives and KPIs.
04
Digital Transformation Roadmap
Sequenced initiatives, target capabilities and implementation plans.
05
Smart Manufacturing Implementation Support
Advisory for automation, connectivity, data and digital governance.
06
Performance & Maturity Improvement
KPI monitoring, maturity reviews and preparation for future reassessment.
07
Official SIRI Assessment Coordination
Preparation and coordination with a Certified SIRI Assessor, where required.
Not sure where to start?
Our team can assess your current maturity across these services and recommend the right roadmap.